Proxy Authentication Setup: Username, Password, and IP Whitelist Checks Before Client Rollout
Proxy authentication setup should be checked before a new client, browser, scraper, or workflow receives live traffic. A connection failure is not always an IP-quality problem. It can come from the wrong authentication method, an expired password, a missing whitelist entry, a protocol mismatch, or a client that is sending requests from a different outbound address than expected.
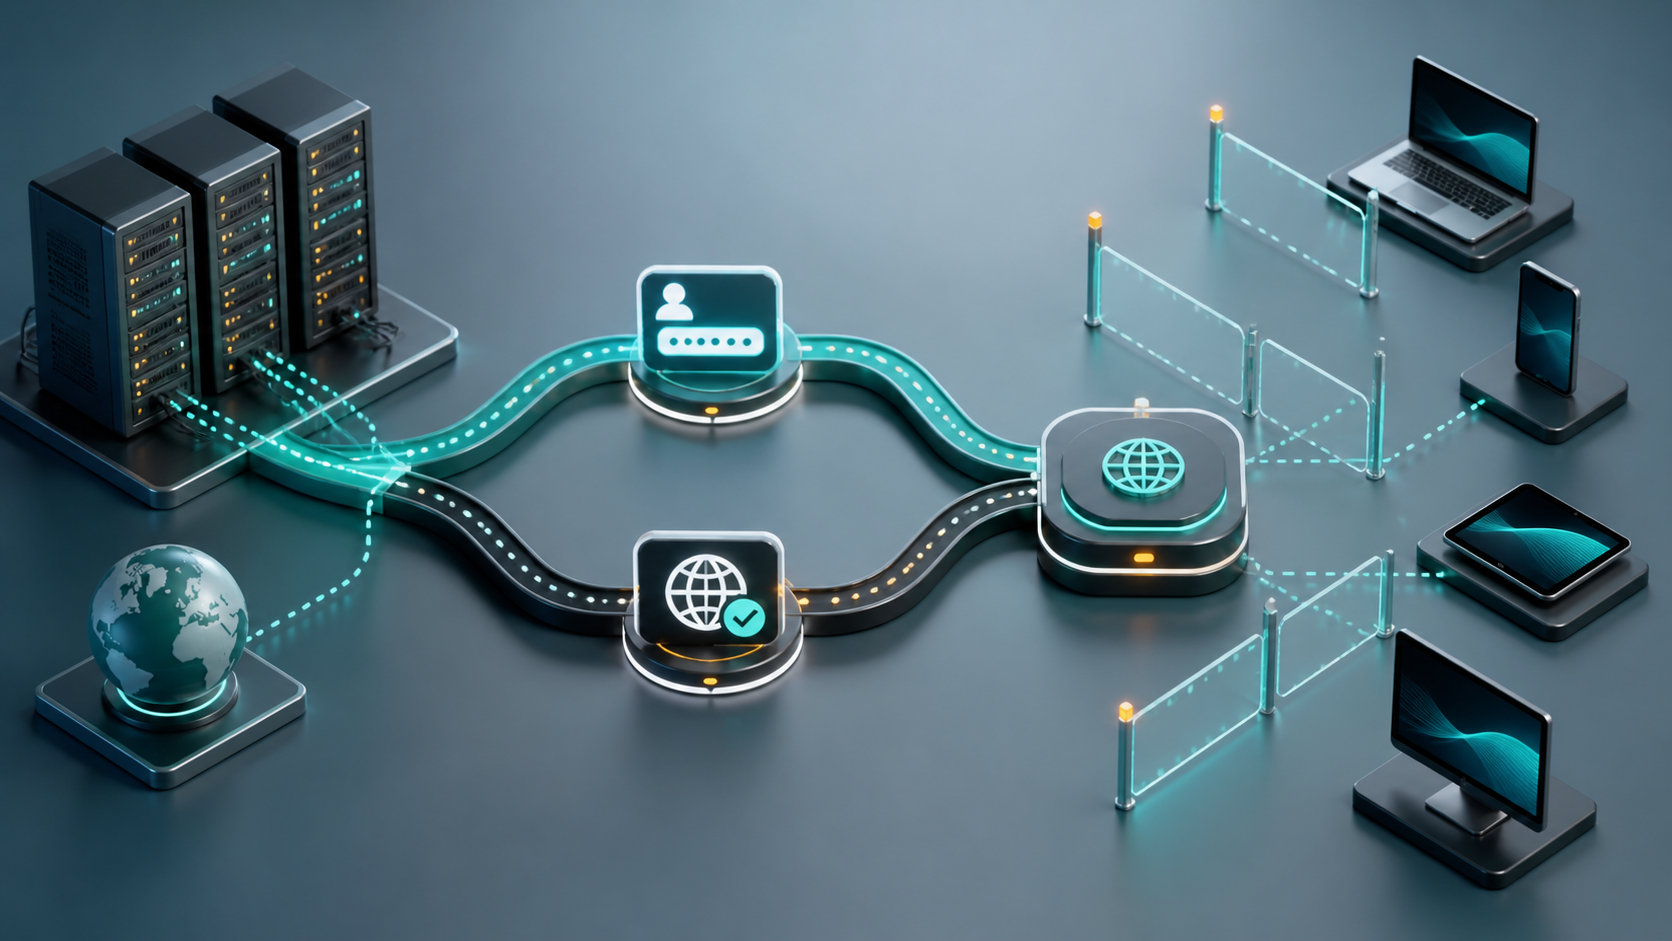
The safest rollout pattern is to verify one authentication path at a time. Confirm username and password access first, confirm IP whitelist access separately, then test the same endpoint from the actual client environment. Do not mix methods during the first check. If two authentication models are active at once, a pass result may hide the method that is really working.
Proxy Authentication Setup Checklist
| Check Area | What To Verify | Pass Condition | Stop Condition |
|---|---|---|---|
| Authentication method | Username/password, IP whitelist, or both | The intended method is documented and isolated | The client can connect but the active method is unclear |
| Credentials | Username, password, port, and endpoint host | Fresh credentials work from a clean test client | 407 errors, repeated login prompts, or copied spaces |
| Whitelist source IP | The real outbound IP of the client environment | The address listed in the dashboard matches the request source | The office, server, VPN, or cloud NAT uses a different address |
| Protocol and port | HTTP, HTTPS, SOCKS5, and matching port | The client sends the right protocol to the right port | Handshake errors, connection refused, or protocol-specific failures |
| Rollout validation | Status code, exit IP, region, DNS behavior, and latency | Repeated checks return stable results | Authentication passes but route behavior is inconsistent |
1. Decide Which Authentication Method The Client Should Use
Start by choosing the authentication model for this rollout. Username and password access is usually easier when clients move between networks, while IP whitelist access can be cleaner for fixed servers or controlled office networks. The choice should match the client environment, not just the proxy dashboard option that looks simplest.
If the project uses residential proxy options, document whether authentication is tied to a port, a region, a session setting, or a pool rule. For team use, keep the selected method in a shared credential inventory so operators do not mix old passwords, stale ports, or outdated whitelist notes.
2. Test Username And Password Access From A Clean Client
For username and password authentication, use a clean test client before adding the proxy to a production workflow. Enter the endpoint host, port, username, and password manually once. Then send a simple request to confirm that the proxy accepts the credentials and returns the expected exit route. This catches copied spaces, old passwords, and wrong-port mistakes before they spread into scripts or browser profiles.
A 407 response usually means the proxy server did not accept the credentials. It does not automatically mean the proxy exit is bad. Before rotating IPs, check whether the username format, password, endpoint, and port match the provider instructions. If the error appears only in one application, compare that application against a command-line or browser test before changing the full proxy pool.
3. Verify The Real Source IP For Whitelist Access
IP whitelist authentication only works when the proxy service sees the same source IP that you added to the whitelist. That sounds simple, but it often fails in real deployments. A laptop may be behind a VPN, an office network may change its public address, and a cloud server may send traffic through a NAT gateway that differs from the address shown inside the server.
Before rollout, open a direct IP-check endpoint from the same client environment that will use the proxy. Record the public source IP, add that exact address to the whitelist, wait for the rule to apply, and retest through the proxy. If the source IP changes between checks, do not treat whitelist authentication as stable for that client until the network path is fixed.
4. Match Protocol, Port, And Client Support
Authentication can be correct while the protocol is wrong. A client configured for SOCKS5 will not behave correctly against an HTTP-only port. Some tools require separate fields for protocol, host, port, username, and password. Others expect a single proxy URL. A small formatting difference can create connection refused errors or silent direct connections.
Use a protocol mismatch checklist when one client works and another does not. Confirm whether the application supports HTTP, HTTPS, and SOCKS5 in the same way, whether DNS resolution happens locally or remotely, and whether authentication is passed during the initial proxy handshake or after a redirect.
5. Retest From The Actual Rollout Environment
A desktop test is not enough if the real rollout will run from a server, automation worker, browser container, or shared team device. Repeat the authentication check from the actual environment. Confirm the exit IP, region, response code, DNS behavior, and latency. If the result differs from the clean local test, the difference is usually in the client network path or application configuration.
For a new region or endpoint, combine the authentication result with an endpoint health check. Authentication tells you whether the proxy accepts the request. It does not prove that the route is suitable for the target task, that DNS behavior is aligned, or that the endpoint can handle the planned traffic volume.
Failure Patterns And What They Usually Mean
| Symptom | Likely Cause | Next Check |
|---|---|---|
| 407 proxy authentication required | Wrong username, password, or auth format | Retype credentials and test with a clean client |
| Connection refused | Wrong port, protocol, or endpoint host | Compare the client setup with the provider endpoint format |
| Whitelist works in one location only | Different source IP or changing network path | Record public source IP from each rollout environment |
| Browser works but script fails | Different proxy URL format or DNS handling | Compare protocol support, DNS mode, and auth passing |
| Authentication passes but target fails | Route quality, region, DNS, or target-side response issue | Run endpoint and target validation before scaling |
6. Set Rollout Stop Conditions Before Adding Traffic
Do not add traffic just because the first request succeeds. Define stop conditions before rollout: repeated 407 errors, changing whitelist source IP, protocol-specific failures, unexpected direct connections, region mismatch, DNS inconsistency, or latency spikes after authentication succeeds. These signals should pause rollout until the cause is isolated.
If timeouts or refused connections appear after authentication is confirmed, follow a client troubleshooting path instead of replacing the proxy immediately. Record the result in a validation record with endpoint, client, auth method, source IP, status code, and final decision.
Final Rollout Record
- Selected authentication method: username/password, IP whitelist, or both with a clear priority.
- Endpoint host, port, protocol, username format, password status, and whitelist source IP.
- Clean-client test result, actual-environment test result, exit IP, region, DNS behavior, and latency.
- Application-specific notes for browsers, command-line tools, scripts, or automation workers.
- Pass condition, stop condition, rollback owner, and the date of the last successful validation.
Proxy authentication setup is a rollout gate, not an afterthought. When teams verify the method, credentials, whitelist source IP, protocol, and actual client behavior in order, they can separate simple setup mistakes from real route problems. That makes the next decision clearer: fix credentials, update the whitelist, correct the client format, retest the endpoint, or pause the rollout before more traffic depends on a weak setup.