Proxy Traffic Segmentation: Separate Login, Validation, Retries, and Scaling Lanes
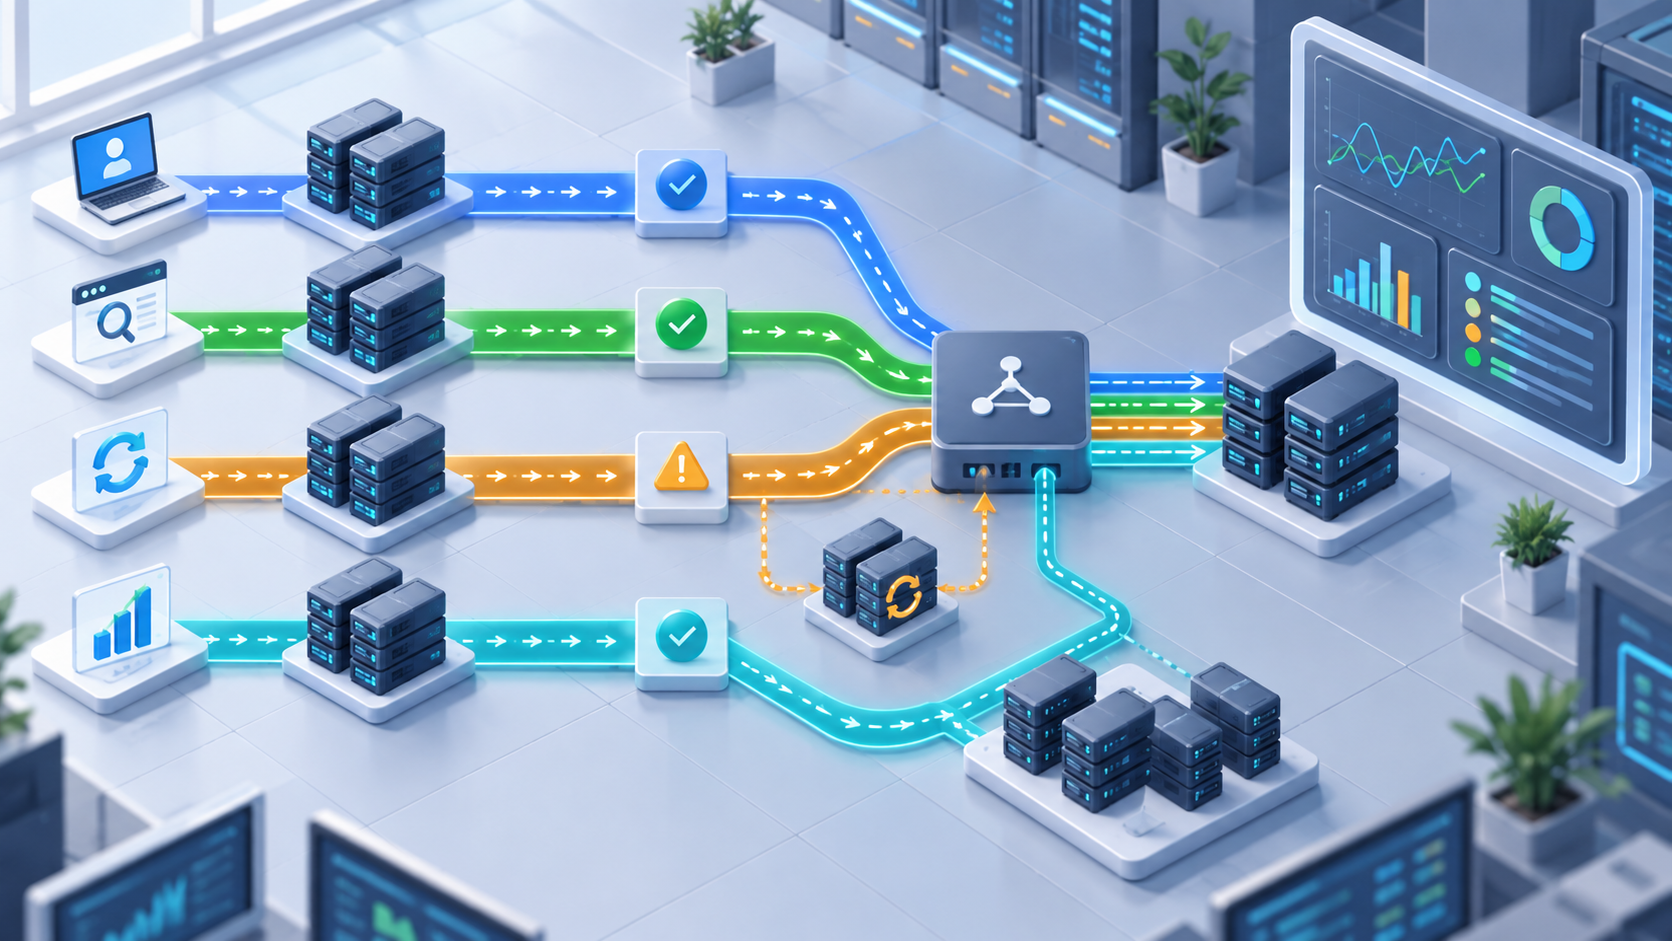
Proxy traffic segmentation means separating different kinds of proxy traffic before they share the same pool, timing rules, and retry policy. Login checks, validation requests, retry traffic, and scaling traffic do not behave the same way. If they are mixed too early, one failure pattern can make the whole proxy pool look unstable.
The practical goal is to give each traffic type its own lane, baseline, stop condition, and review record. A login lane should stay conservative. A validation lane should test fields and readiness. A retry lane should contain failures. A scaling lane should only receive exits that already passed calm checks. This structure keeps proxy troubleshooting from turning into guesswork during rollout.
Why Proxy Traffic Needs Separate Lanes
Different proxy tasks create different signals. A login request may be sensitive to location, session continuity, and timing. A validation request may only need to prove that the endpoint, protocol, DNS path, and target response are usable. A retry request may be useful in small amounts but harmful when it loops. A scaling request tests whether the pool can handle a larger window without changing status codes or response timing.
For teams using residential proxies, segmentation is especially useful because residential exits are often assigned to more sensitive account or region workflows. The point is not to make every lane complex. The point is to keep a fragile lane from being judged by the same traffic pattern as a high-volume test lane.
A Simple Segmentation Model
| Traffic Lane | Primary Job | Key Fields | Stop Condition |
|---|---|---|---|
| Login lane | Check whether the account or client can enter a stable session | Exit IP, region, protocol, authentication, session state, first response time | Region drift, authentication failure, or repeated login interruption |
| Validation lane | Confirm that a proxy endpoint is ready for controlled use | Protocol, DNS path, target URL, status code, latency, content response | Unstable endpoint, wrong region, DNS conflict, or repeated timeout |
| Retry lane | Recover from occasional failure without amplifying load | Retry count, backoff, final status, failure reason, quarantine rule | Retries repeat the same failure or create a larger request wave |
| Scaling lane | Increase traffic only after baseline checks are stable | Concurrency, request spacing, success rate, error cluster, rollback point | Latency spikes, status changes, or grouped timeouts appear during ramp |
Start With The Login Lane
The login lane should be the most conservative lane. It should not inherit retry pressure or burst timing from larger tests. Before a proxy is used for login-like tasks, confirm the protocol, host, port, authentication method, exit region, and basic response behavior. If credentials or IP whitelist rules are involved, run an authentication setup check before sending real session traffic.
The login lane should also have a clear stop rule. Stop when the endpoint changes region unexpectedly, authentication fails repeatedly, session state becomes inconsistent, or the first response pattern looks different from the validation lane. Do not push more traffic through the same exit until the cause is separated.
Use The Validation Lane Before Scaling
The validation lane is where new endpoints prove they are ready. It should be low volume, repeatable, and field-driven. Record protocol, authentication result, assigned exit IP, region, DNS behavior, target response, status code, redirect path, and latency. A validation pass is not the same as a scaling pass; it only says the endpoint is healthy enough for the next stage.
When adding a new region or endpoint group, use an endpoint health check before mixing that traffic with existing lanes. If validation fails, keep the endpoint out of the login and scaling lanes until the failure reason is clear.
Keep Retry Traffic Contained
Retry traffic needs its own lane because retries can hide the original failure. A request that fails once may be normal. A request that fails, retries too quickly, and enters the same proxy exit again can create a larger failure wave. When retry traffic is mixed into normal traffic, the pool may look worse than it is.
Use a retry storm checklist to cap attempts, add backoff, quarantine repeated failures, and prevent the same bad request from returning immediately to the same pressure window. Retry success should be measured by clean recovery, not by the number of attempts made.
Only Send Stable Exits To The Scaling Lane
The scaling lane should receive only endpoints that already passed calm validation. Before volume increases, compare the current behavior with a request timing baseline. If the calm path is unstable, scaling only adds noise. If the calm path is stable, raise request count, concurrency, or spacing pressure one variable at a time.
The scaling lane should not make rotation decisions by itself. It should record what changed first: latency, status codes, retry queue, timeout clusters, or target response. Then the operator can decide whether to slow down, quarantine a small group, adjust retry rules, or rotate the exit group.
Decision Table For Moving Traffic Between Lanes
| Observation | Likely Meaning | Move Or Hold? |
|---|---|---|
| Endpoint passes validation but fails during login | Session, account, region, or authentication context may be different | Hold in login lane and review session fields |
| Endpoint fails validation repeatedly | Protocol, DNS, region, or target response is not ready | Do not move to login or scaling lanes |
| Retry lane repeats the same failure | Retries are amplifying the original issue | Quarantine or slow down before sending traffic back |
| Scaling lane fails only during bursts | Concurrency or request spacing is too aggressive | Return to baseline and reduce pressure |
| All lanes show the same failure | Endpoint, route, or target response may be broadly weak | Compare another exit group before replacing the pool |
Record Each Lane Separately
Segmentation only works if the records stay separate. A good log should show which lane produced the signal, what changed, which endpoint was used, and what action followed. Without that separation, a login issue may be mistaken for a pool-wide quality problem, or a retry issue may be mistaken for a bad proxy exit.
A change log template helps preserve the decision trail. Add lane name, entry condition, exit condition, failure reason, rollback decision, and next test window. These fields make it easier to explain why a proxy was kept, slowed down, quarantined, or moved to scaling.
A Practical Rollout Sequence
- Validate the endpoint with low-volume checks before assigning it to any sensitive workflow.
- Send login-like traffic only after protocol, authentication, region, and response behavior are stable.
- Route failures into a retry lane with a capped attempt count and backoff policy.
- Move only stable endpoints into scaling, and raise one pressure variable at a time.
- Record lane, exit IP, target path, timing, status code, failure reason, and next action.
- Return traffic to a calmer lane when two signals fail in the same scaling window.
When Segmentation Is Worth The Extra Work
Small one-off checks may not need a formal segmentation model. But segmentation becomes valuable when the same proxy pool supports multiple tasks, regions, clients, or rollout stages. It is also useful when failures are expensive to misread: login interruption, region mismatch, retry overload, or a scaling window that affects many requests.
If your team already uses a proxy service option across validation, login, retry, and scaling workflows, segmentation gives those workflows cleaner boundaries. It helps you decide whether the next move is to slow down, quarantine, rotate, retest, or keep the current exit group in place.
Proxy traffic segmentation is not bureaucracy. It is a way to keep one failure mode from contaminating the whole proxy pool. When each lane has its own purpose, fields, and stop rule, proxy troubleshooting becomes calmer, faster, and easier to repeat.