Proxy TLS Handshake Fails: Separate CONNECT, SNI, and Certificate Trust Errors
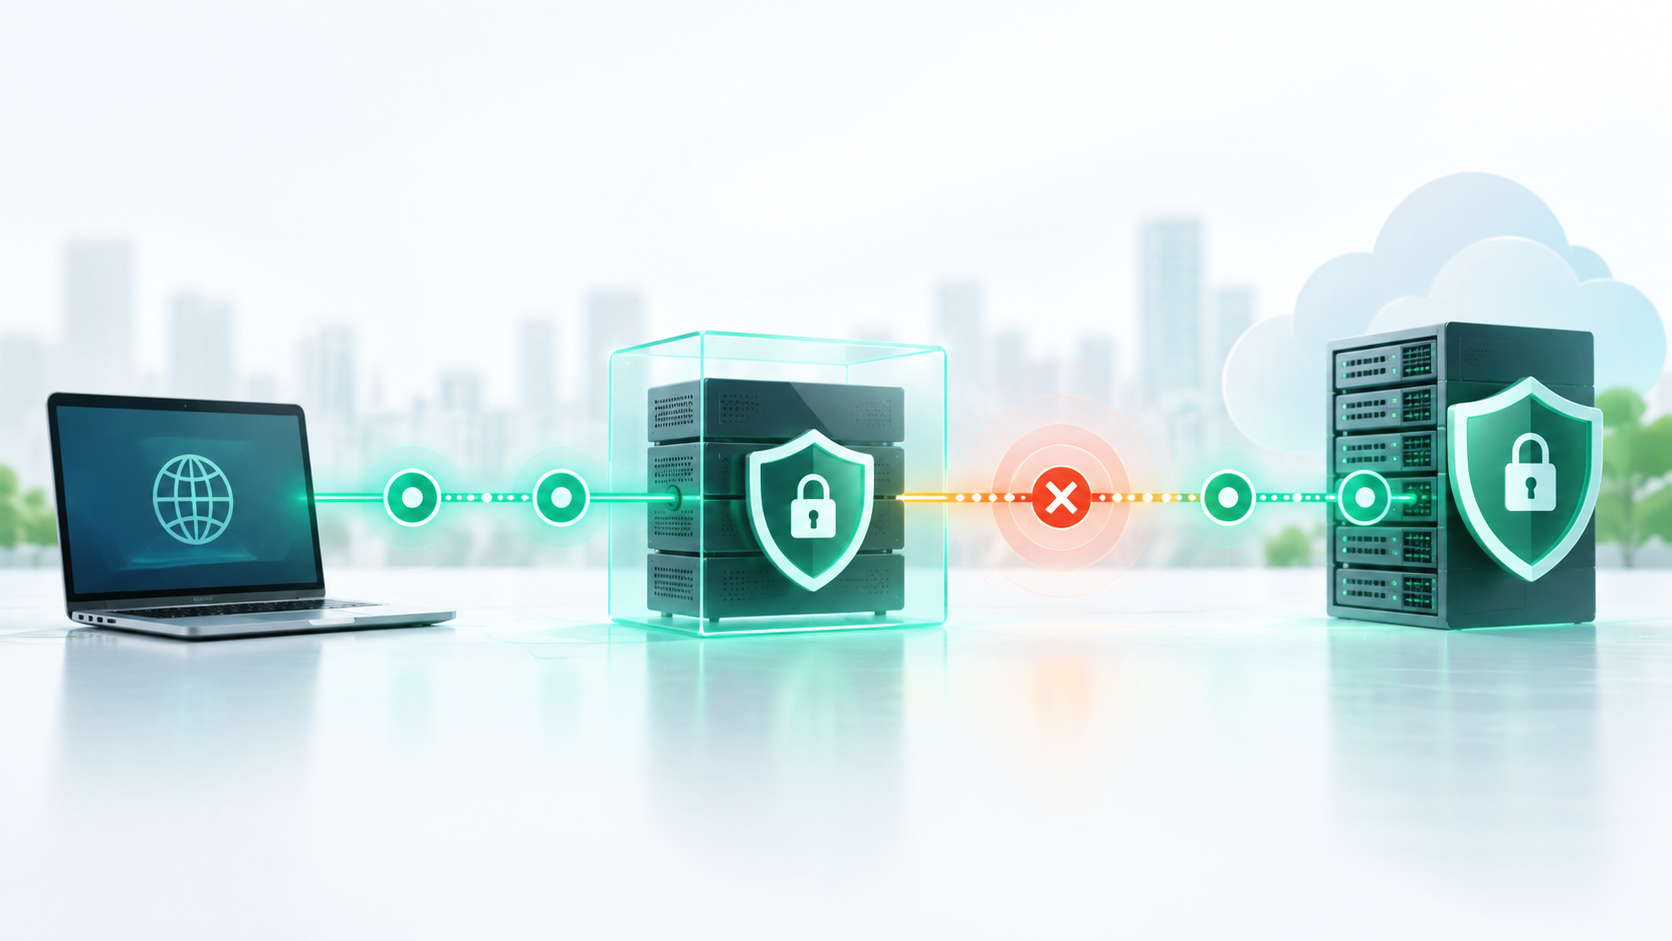
A TLS handshake failure through a proxy does not automatically mean the exit IP is bad. The failure can occur before the encrypted session begins: the client may fail to establish the proxy tunnel, send the wrong hostname for SNI, receive an unexpected certificate chain, use a trust store that differs from the browser, or negotiate a TLS version the upstream endpoint does not accept.
The fastest diagnosis is to separate the proxy connection from the TLS negotiation. Record the proxy protocol, proxy host and port, authentication result, target hostname, CONNECT or SOCKS response, DNS mode, TLS alert, certificate subject and issuer, client library, and test time. Then compare a direct request with a proxied request to the same hostname. Do not disable certificate verification or install an unknown root certificate to make the error disappear.
Classify the failure before changing the proxy exit
| Observed result | Likely layer | First evidence to collect |
|---|---|---|
| 407 or authentication error before TLS starts | Proxy authentication | Proxy response code and active credential scope |
| CONNECT denied or tunnel cannot be created | Proxy protocol, target port, or policy | CONNECT response and requested host:port |
| Certificate name does not match the target | SNI, DNS, or wrong upstream endpoint | Requested hostname and certificate SAN entries |
| Unknown certificate authority | Trust store, incomplete chain, or approved inspection gateway | Full certificate chain and issuer |
| Protocol version or cipher alert | TLS policy mismatch | Client TLS version, cipher support, and upstream requirement |
| Browser works but code fails | Client library, CA bundle, or proxy URL handling | Library version, transport adapter, and trust-store path |
1. Prove that the proxy tunnel exists before testing TLS
For an HTTPS target over an HTTP proxy, the client normally asks the proxy to create a CONNECT tunnel to the target host and port. TLS begins only after the proxy accepts that tunnel. For SOCKS5, the client first completes the SOCKS negotiation and target connection. If authentication, protocol selection, or target-port policy fails, the resulting client message may look like a TLS failure even though no TLS handshake occurred.
Capture the proxy response before the handshake. Use the existing protocol mismatch checks to verify the proxy scheme, endpoint, target port, DNS mode, and client support. If the response is 407, validate the credential format and whitelist state with the authentication setup checklist. Do not troubleshoot certificates until the tunnel step passes.
2. Compare direct and proxied handshakes to the same hostname
Run a direct request and a proxied request from the same device and client version, using the exact same target hostname. Record whether each path reaches TLS, the negotiated TLS version, certificate subject, issuer, validity dates, and final error. A direct failure and a proxy failure point toward the target, local trust store, or shared client policy. A direct pass with a proxy-only failure narrows the problem to the tunnel path, proxy exit, DNS path, or inspection layer.
Keep the request small and repeatable. Do not compare different subdomains, redirects, or application accounts in the first pass. If the error changes between timeout, reset, and TLS alert, follow the timeout versus connection-refused diagnosis first so transport instability is not misreported as a certificate problem.
3. Preserve the hostname so SNI reaches the correct upstream
Modern HTTPS endpoints often host multiple domains on one address. During TLS negotiation, SNI tells the server which hostname the client expects. If a client connects by IP address, rewrites the target hostname, sends an empty SNI value, or resolves to the wrong upstream, the server may return a default certificate that does not match the requested domain.
Record the URL hostname, CONNECT target, DNS answer, SNI name, and certificate Subject Alternative Name entries. A pass requires the requested hostname to appear in the certificate scope and the same hostname to be used through the tunnel. If only an IP-based test fails, repeat with the hostname instead of treating the certificate as invalid.
4. Read the entire certificate chain, not only the leaf certificate
A certificate can match the hostname and still fail validation if the intermediate chain is missing, the root is not trusted, the certificate is expired, or the client clock is wrong. Save the leaf and intermediate certificate metadata from both direct and proxied paths. Compare subject, issuer, validity dates, SAN entries, and chain order.
If the browser passes while a command-line client or application fails, confirm which CA bundle each one uses. Browsers and operating systems may update trust roots differently from container images, language runtimes, and embedded libraries. Updating an approved CA bundle is different from disabling verification; keep verification enabled throughout the test.
5. Detect certificate replacement without assuming malicious behavior
Some approved enterprise gateways inspect TLS and issue a replacement certificate from an internal authority. Public proxy routing should not require an unexplained certificate replacement. Compare the direct and proxied issuers. If the proxy path presents a different chain, confirm whether that behavior is documented, approved, and limited to the expected environment.
Stop if the replacement issuer is unknown, the certificate scope does not match the target, multiple unrelated domains return the same unexplained certificate, or the route asks users to install an unverified root. Preserve the chain, timestamp, proxy endpoint, and target hostname before isolating the route. Do not send credentials or sensitive payloads through an unexplained certificate path.
6. Check TLS versions, ciphers, and client-library behavior
An older runtime may offer only deprecated TLS versions or a cipher set the upstream no longer accepts. A newer client may enforce stricter certificate or hostname validation than an older browser. Record the client and TLS library versions, enabled minimum and maximum TLS versions, negotiated protocol on the direct path, and the alert returned on the proxy path.
Also confirm that the library supports the configured proxy scheme. An HTTP proxy URL, HTTPS proxy transport, and SOCKS5 proxy are not interchangeable in every client. If one known-good client passes and another fails, compare proxy URL parsing, DNS behavior, CA bundle, SNI support, and transport adapter before changing exits.
7. Include DNS, IPv4, and IPv6 in the path comparison
Direct and proxied requests may resolve the target through different DNS systems or address families. One path can reach an IPv4 endpoint while another reaches IPv6, a different region, or an outdated edge node. Record local DNS results, remote DNS results when the proxy supports them, the connected address family, and the certificate returned by each path.
Do not force a different address family as a permanent fix without evidence. Use one controlled IPv4 test and one controlled IPv6 test where supported. If only one path fails, report it as an address-family or endpoint difference and verify the upstream route before changing the entire proxy pool.
8. Use pass, fail, ambiguous, and stop outcomes
| Outcome | Evidence | Decision |
|---|---|---|
| Pass | Tunnel succeeds, hostname matches, chain validates, and a low-risk request completes | Resume traffic gradually |
| Proxy setup failure | Authentication or CONNECT/SOCKS negotiation fails before TLS | Repair protocol, port, credentials, or policy |
| Trust failure | Hostname is correct but the chain is incomplete or the approved root is absent | Repair the CA bundle or upstream chain |
| SNI or endpoint failure | The returned certificate belongs to another hostname | Correct hostname, DNS, or target routing |
| Ambiguous | Different clients receive different chains or alerts | Compare library, trust store, DNS mode, and TLS policy |
| Stop | Unknown certificate replacement or unexplained issuer persists | Isolate the route and do not send sensitive data |
9. Retest in a small lane without weakening verification
Retest one target through one proxy endpoint with one known-good client. Confirm proxy authentication, tunnel creation, target hostname, certificate chain, TLS version, handshake time, first-byte time, and final response class. Compare timing against the normal request timing baseline so a slow handshake is not confused with a failed one.
Keep hostname and certificate verification enabled. Stop the rollout if the tunnel response changes unexpectedly, the issuer remains unexplained, the target hostname does not match, or retries begin multiplying. Changing several settings at once destroys the comparison; make one repair, repeat the same test, and record the result.
10. Keep a compact TLS failure record
- Proxy protocol, host, port, and authentication result
- Target hostname, port, CONNECT or SOCKS response
- Local or remote DNS result and connected address family
- Direct-path and proxy-path TLS alerts
- Certificate subject, issuer, SAN entries, and validity dates
- Client, TLS library, and CA bundle versions
- Negotiated TLS version and handshake duration
- Repair attempted, retest result, and stop decision
Use a proxy error log to keep the tunnel response and TLS evidence together. For broader setup decisions, compare proxy setup options by supported protocols, authentication, DNS behavior, session controls, and operational visibility. A useful setup makes each failure layer observable instead of reducing every error to “proxy not working.”
Conclusion: prove the tunnel before repairing the handshake
When a proxy TLS handshake fails, first prove whether the proxy tunnel was created. Then compare direct and proxied handshakes, preserve the target hostname for SNI, inspect the full certificate chain, and compare trust stores, TLS policies, DNS paths, and client libraries. Each layer has a different repair and a different pass condition.
The reliable sequence is to keep verification enabled, change one variable at a time, retest in a small lane, and stop when the certificate path cannot be explained. Replacing exits repeatedly or suppressing certificate checks adds noise and can hide the actual boundary where the connection fails.