HTTP 401 Through a Proxy: Check WWW-Authenticate, Token Scope, and Redirects
An HTTP 401 response through a proxy usually means the target service did not accept the request’s identity. It is different from HTTP 407, which asks the client to authenticate to the proxy. Before changing the exit IP, identify which hop returned the response, read the target’s WWW-Authenticate header, and preserve one low-risk request with sensitive values removed.
For a useful first pass, record the timestamp, requested URL, method, final host, status, authentication scheme, redirect chain, token expiry metadata, proxy endpoint, and exit address. Never place full passwords, authorization tokens, or session values in a shared log. Stop retrying if credential ownership, destination, or permission cannot be confirmed.
Separate 401, 403, 407, and 429 before changing anything
| Status | Primary meaning | Evidence to inspect | Do not assume |
|---|---|---|---|
| 401 | The target did not accept the presented identity | WWW-Authenticate, token scope, session, target URL | The proxy is unavailable |
| 403 | The target recognized the request but denies the resource | Account permissions, resource policy, documented restrictions | A new IP grants permission |
| 407 | The proxy requires authentication | Proxy-Authenticate, credentials, allowlist, client syntax | The target login is wrong |
| 429 | A rate or quota boundary was reached | Retry-After, concurrency, request rate, quota | Immediate retries are harmless |
If the response is 407, move to the 407 proxy authentication guide. If the proxy connection never completes, verify the account, protocol, endpoint, and allowlist with the proxy authentication setup checklist before testing target credentials.
1. Identify the hop that returned the 401
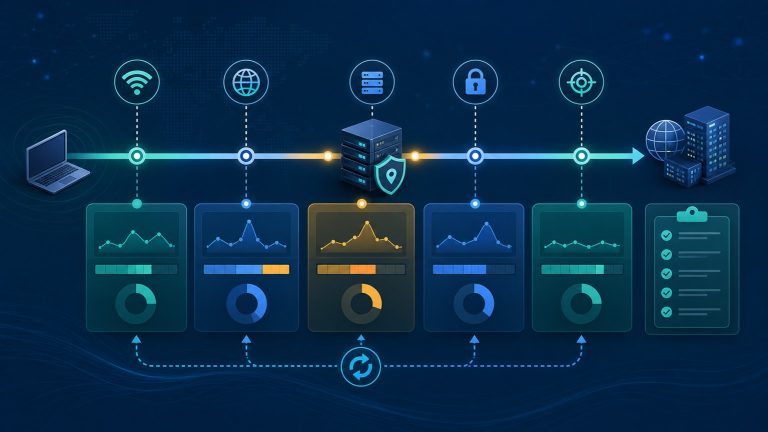
Capture the full response chain with automatic redirects disabled for one controlled request. Compare the response host, Server, Via, Location, WWW-Authenticate, and any proxy-authentication header. A 401 from the intended target host belongs in the target-authentication branch. A response from a proxy gateway or unexpected intermediary belongs in the network or proxy-authentication branch.
A pass is a chain whose response owner is unambiguous. A fail is a chain that only exposes a final browser page. An ambiguous result is a response whose host and headers disagree; stop before sending credentials and have the route owner confirm the authentication boundary.
2. Read WWW-Authenticate before editing credentials
The WWW-Authenticate header tells the client which authentication scheme the target expects and may include a realm or error detail. Record the scheme and realm without capturing the secret. Confirm that the client sends the matching type, such as Basic, Digest, or Bearer, to the intended host and path.
If the target publishes an authentication specification, use it as the source of truth. Do not repeatedly guess header formats. A request can be syntactically valid yet rejected because it uses the wrong scheme, realm, audience, or endpoint.
3. Keep proxy credentials and target credentials separate
Proxy credentials authorize the client to use the proxy service. Target credentials authorize access to the destination application. They can both be usernames and passwords, but they belong in different connection stages and headers. Never place a target token in a proxy URL or submit a proxy password to the target login endpoint.
Test a public, non-authenticated target resource through the same fixed endpoint. If that resource succeeds and the protected resource returns 401, the upstream connection is working and the investigation should remain at the target-authentication layer.
4. Check token expiry, audience, and scope
For token-based access, compare the issued-at time, not-before time, expiry, audience, issuer, and scope with the target resource. Record only non-secret metadata and a short redacted identifier. A token for one API, region, tenant, or environment may be rejected by another even when its signature and format are valid.
Also verify system time. A large clock difference can make a fresh token appear not yet valid or already expired. If refreshing through the approved flow restores access, document the expiry path rather than treating an exit change as the repair.
5. Inspect session expiry without reusing session data
Record the last successful request, login time, expected session lifetime, first 401 time, and whether the exit changed during the flow. Re-establish an expired session only through the target’s normal login or refresh process. Do not copy cookies or session values between users, devices, or proxy exits.
Use the session continuity checklist when the 401 appears after a reconnect or endpoint change. Compare domain, path, secure and same-site attributes, expiry, callback state, and exit continuity without exposing values.
6. Follow redirects and check where Authorization disappears
Many clients intentionally remove the Authorization header when a redirect crosses hosts, schemes, or security boundaries. Capture each status and Location value, then compare the request headers sent at the original URL and the final protected URL. Do not force credentials across an untrusted redirect.
If authentication vanishes during a repeating login or callback sequence, use the redirect-loop evidence guide to identify the exact host or scheme transition. Stop if the chain leaves the approved domain set.
7. Compare method, path, and request headers
A public page, login endpoint, API route, and tenant-specific path may enforce different authentication rules. Keep the method, full path, query, host, content type, accepted response type, and documented origin fields consistent. Check whether the client removes, duplicates, or rewrites the authorization header before the request reaches the target.
When a browser succeeds but a script fails, compare the actual requests rather than the visible page. The difference may be a preflight request, callback, required header, session refresh, or redirect policy. Redact all secret values before storing the comparison.
8. Run a direct-versus-proxy comparison
Use the same approved test account, client version, target resource, request method, and time window. Send one direct request and one request through a fixed proxy endpoint. Compare the response owner, status, WWW-Authenticate scheme, redirect chain, request-header behavior, final host, and timing.
If both paths return the same 401, focus on credentials, token metadata, session state, or target availability. If only the proxied path fails, inspect cross-host redirects, header preservation, regional entry points, and the target’s documented session constraints. One comparison establishes a lead, not a proven root cause.
9. Apply pass, fail, ambiguous, and stop conditions
| Outcome | Evidence | Next action |
|---|---|---|
| Pass | Two controlled requests reach the protected resource with the expected identity | Resume gradually and retain the redacted record |
| Fail: expired state | The approved refresh flow consistently restores access | Repair session refresh or token renewal timing |
| Fail: target identity | Direct and proxy paths return the same 401 | Verify credentials, audience, scope, and target status |
| Fail: route-specific | Only the fixed proxied path loses authentication on a known hop | Inspect redirect and header policy at that boundary |
| Ambiguous | Identical attempts alternate between success and 401 | Compare time, endpoint, DNS, region, and session inputs |
| Stop | Credentials are unverified, account lockout appears, or the route leaves approved domains | Stop retries and escalate with redacted evidence |
10. Limit retries and protect the diagnostic signal
Set a small maximum attempt count and pause after any account-lockout warning, rate-limit response, or changing challenge. Parallel retries make it harder to associate one credential state with one response and can turn an authentication problem into a rate-limit incident.
Keep one fixed endpoint during diagnosis. Rotating exits, changing clients, refreshing credentials, and clearing state in the same attempt destroys the comparison. Record each attempt in a proxy error log template with secrets removed.
11. Change the proxy route only after authentication checks pass
A route-isolation test is useful only when direct access succeeds, a fixed proxied path repeatedly returns 401, and the authentication scheme, credentials, token scope, session, path, request headers, and redirects have already been compared. Keep every other input fixed when testing a second endpoint.
When reviewing proxy service options, choose an endpoint whose protocol, region, session behavior, and history can be recorded. Changing the route is a diagnostic step, not a substitute for target authorization and not proof that the previous exit was defective.
Conclusion: locate the authentication boundary first
To diagnose HTTP 401 through a proxy, identify the response owner, read WWW-Authenticate, separate proxy and target credentials, check token and session timing, follow redirects, compare request headers, and run a controlled direct-versus-proxy test. Keep the endpoint and request fixed until the failing boundary is reproducible.
A useful incident record includes time, URL, method, response owner, authentication scheme, redacted token metadata, redirect chain, proxy endpoint, exit address, pass criteria, and stop decision. That evidence lets application, network, and proxy owners investigate the same failure without exposing credentials or masking it with repeated exit changes.