HTTP 405 Through a Proxy: Check Allowed Methods, Redirects, and Gateway Rewrites
An HTTP 405 Method Not Allowed response through a proxy means a server or intermediary understood the request method but will not accept that method for the selected resource. It does not, by itself, prove that the proxy exit is blocked or that a new IP will fix the request.
Before changing the route, preserve the exact URL, method, redirect history, status, Allow header, safe request-header summary, proxy protocol, endpoint, exit address, and timestamp. The immediate job is to identify who returned 405, determine which methods the resource accepts, and test whether a redirect or gateway changed the request.
Use the first comparison to locate the method rejection
| Observed result | Leading branch | Evidence to preserve | Next action |
|---|---|---|---|
| Direct and proxy paths return the same 405 | Target route or application policy | Allow header, route, method, server marker | Use a documented allowed method |
| Only the proxy path returns 405 | Gateway rule, redirect, or method rewrite | Hop-by-hop method and Location chain | Compare one fixed request on both paths |
| OPTIONS fails while the final method works in a non-browser client | Preflight or route configuration | Origin, requested method, allow headers | Check the browser preflight branch |
| POST becomes GET after a redirect | Client redirect behavior | Status chain, final URL, method per hop | Disable redirects and inspect each hop |
| No HTTP response is received | DNS, connect, protocol, or TLS | Resolver, socket, handshake, timeout | Resolve transport before 405 |
If there is no HTTP response, start with the proxy protocol mismatch guide. A CONNECT, TLS, or SOCKS negotiation failure is not an HTTP method rejection.
1. Capture the response owner and the Allow header
Record the final host, status line, Allow, Server, Via, request identifier, Date, and the first safe lines of the response body. The Allow header should describe methods accepted by the resource, but some systems omit it or generate it at a gateway. Treat it as evidence, not as the only proof of ownership.
A pass is a repeatable 405 whose response owner and allowed-method list agree. A fail is a screenshot without the original URL, method, or headers. An ambiguous result is a response whose gateway markers and target markers conflict; stop broad retries until the boundary is confirmed.
2. Build one direct-versus-proxy control
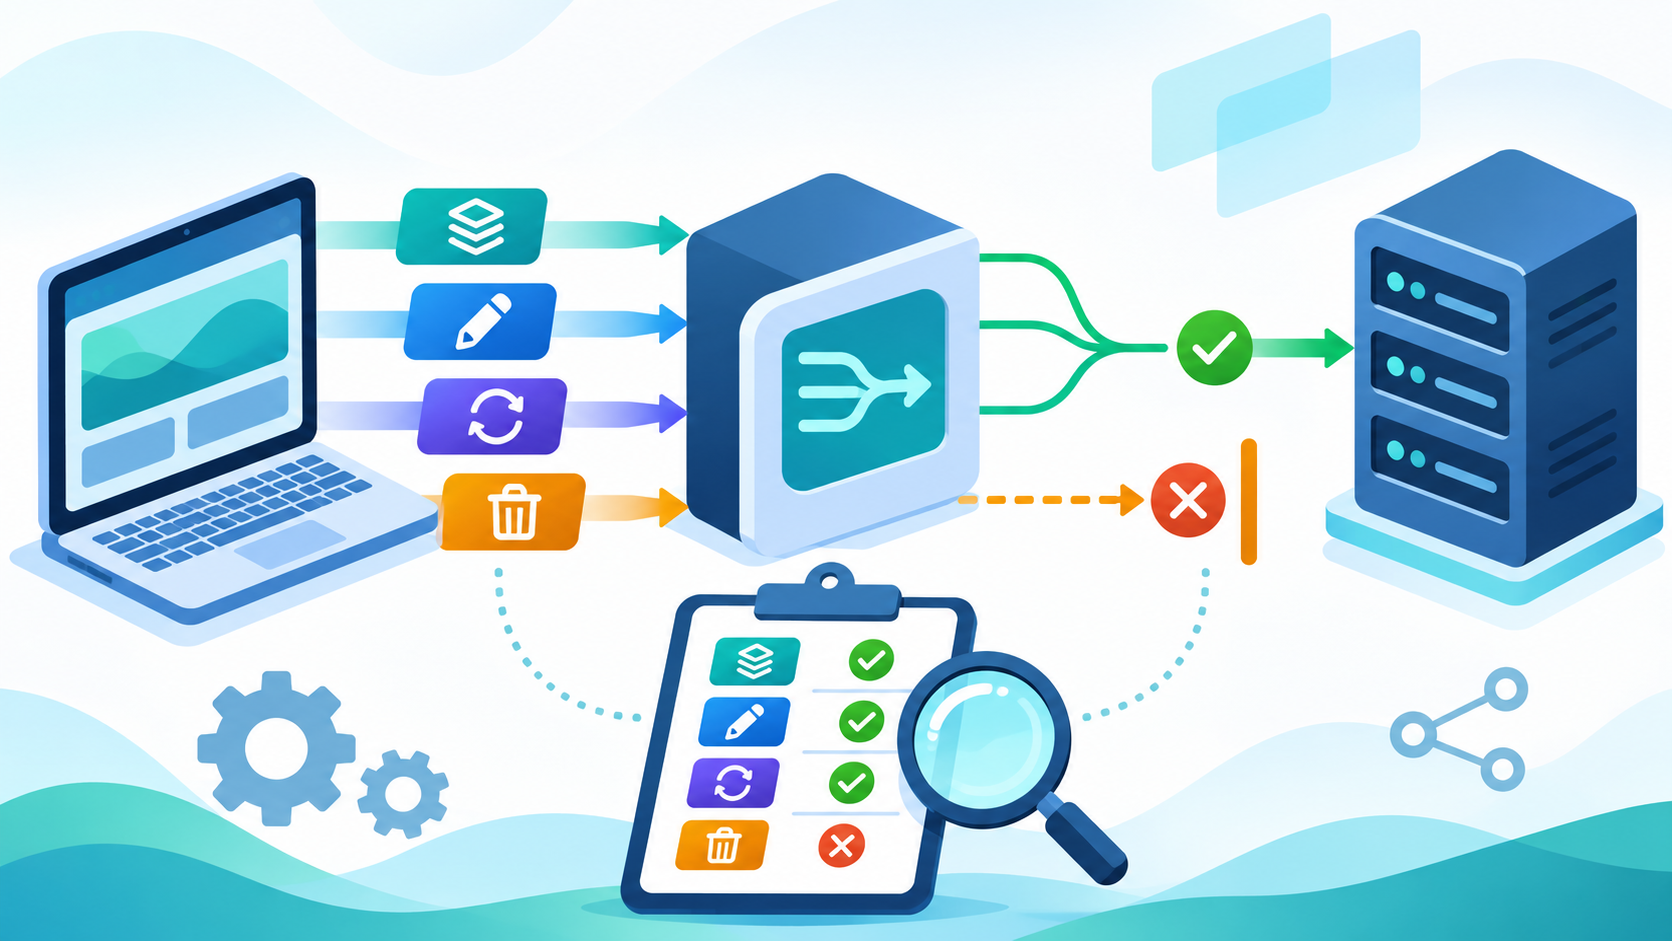
Fix the client version, URL, method, headers, body, redirect setting, and time window. Send one direct request and one request through a fixed proxy. Disable automatic redirects and retries, then record the status, response owner, Allow value, final URL, exit address, and method used on every hop.
If both paths return the same 405, the route or application policy is the leading branch. If only the proxy path fails, inspect the gateway, redirect chain, and request transformation. One pair is a diagnostic lead, not proof that every exit behaves the same way.
3. Verify the endpoint and method against the current interface contract
Confirm that the final path actually supports the method being sent. A collection path may accept POST while an item path accepts GET, PATCH, or DELETE; a read-only page may accept only GET and HEAD. Check current first-party documentation or the service owner rather than guessing method names.
Test the smallest documented request. Do not change the path, method, body, and proxy exit in one attempt. If the minimal documented request succeeds, restore optional headers and body fields one at a time.
4. Inspect redirects without letting the client rewrite the method silently
Some clients change POST to GET after particular 301 or 302 responses, while 307 and 308 are intended to preserve the method. Libraries and browser versions may differ. Disable automatic redirect following, record each Location, and note the method actually sent at every hop.
If the 405 appears only after a redirect, use the redirect loop diagnosis to compare scheme, host, path, session state, and redirect behavior. Do not copy authorization headers to a different host unless the service specification explicitly requires it.
5. Separate browser preflight failures from final-request failures
A browser may send an OPTIONS preflight before the final request. Capture the Origin, requested method, requested headers, preflight status, and response allow headers. If OPTIONS returns 405, the final request may never be sent even though the same final method works in a command-line client.
Do not add permissive cross-origin headers blindly. The application or gateway owner should define the approved origins, methods, and headers. The diagnostic goal is to show whether the failure occurs on preflight or on the final method.
6. Check HEAD and health-check assumptions
Monitoring tools often use HEAD to avoid downloading a full response, but not every route implements HEAD correctly. If HEAD returns 405 while GET succeeds, record that difference and configure the health check to use a supported read-only method or a dedicated health endpoint.
Use the proxy endpoint health checks to keep transport health separate from application-method support. A healthy proxy can carry a request that the target route still rejects.
7. Look for gateway method allowlists and rewrites
Reverse proxies, web application firewalls, and API gateways may allow only a configured method set or route methods to different upstream handlers. Compare the method seen by the client, the method logged at the gateway, and the method received by the application when administrative logs are available.
Do not infer a private gateway rule from the status alone. If only the proxy path returns 405, preserve the gateway request identifier and ask the route owner to confirm whether a method policy or rewrite executed.
8. Keep malformed-request and media-type errors in their own branches
A malformed URL, conflicting length headers, or invalid body framing normally belongs to a 400 branch. An unsupported body format may produce 415. If the status changes after correcting the method, use the HTTP 400 request checklist rather than continuing to label every failure as 405.
9. Run a bounded retest without rotating variables
For a read-only request, make one retest with the documented method and redirects disabled. For state-changing methods, confirm whether the service processed the original request before repeating it. Keep the endpoint and fixed proxy unchanged so the result remains comparable.
Stop when the method contract is unknown, the response owner is ambiguous, a state-changing result cannot be confirmed, or the status changes to a different error class. Parallel retries and rapid exit rotation erase the evidence.
Pass, fail, ambiguous, and stop conditions
| Retest result | Decision | Action |
|---|---|---|
| Documented method succeeds on both paths | Pass | Restore traffic gradually and keep the record |
| Unsupported method returns 405 with a consistent Allow header | Expected rejection | Use an approved method or endpoint |
| Direct succeeds but fixed proxy fails with a changed method or route | Proxy-path transformation | Escalate with hop-by-hop evidence |
| Preflight fails but the final request is never sent | Preflight branch | Repair approved route policy, then retest once |
| Response owner or state-changing result is unknown | Stop | Disable retries and confirm with the service owner |
10. Record enough evidence for another operator to reproduce the test
Record the timestamp, client, URL, method, redirect setting, method per hop, safe header summary, body type, proxy protocol, endpoint, exit address, status, Allow value, response owner, request identifier, and final decision. The proxy error log template provides a consistent handoff format.
Use method evidence before changing the proxy route
A reliable HTTP 405 workflow is: capture the response owner and allowed methods, reproduce one fixed direct/proxy pair, verify the endpoint contract, inspect redirects and preflight, compare gateway and application methods, then run one bounded retest. Use proxy service options for a controlled route comparison only after the evidence points to the proxy path.